SecurityEC-Council
Learning Notes
Ethical Hacking Essentials
Strengthened offensive-security awareness to better design defensive controls and secure development practices.
Attack surface mappingExploit pathsSecure SDLC
What I Learned
- Understand attacker mindset to identify weak points before exploitation.
- Translate common exploit patterns into stronger application safeguards.
- Integrate security checks earlier in the software lifecycle.
How I Applied This
- Used threat scenarios to prioritize high-risk fixes during development.
- Added secure coding checkpoints before production deployment.
- Improved vulnerability response speed with clearer severity mapping.
Learning Diagram
Ethical Hacking Learning Diagram
A practical cycle from reconnaissance to remediation that I use to strengthen application security posture.
Reconnaissance
Enumeration
Vulnerability analysis
Controlled exploitation
Impact assessment
Remediation plan
Security verification
Secure release
Each release starts the next round of reconnaissance.
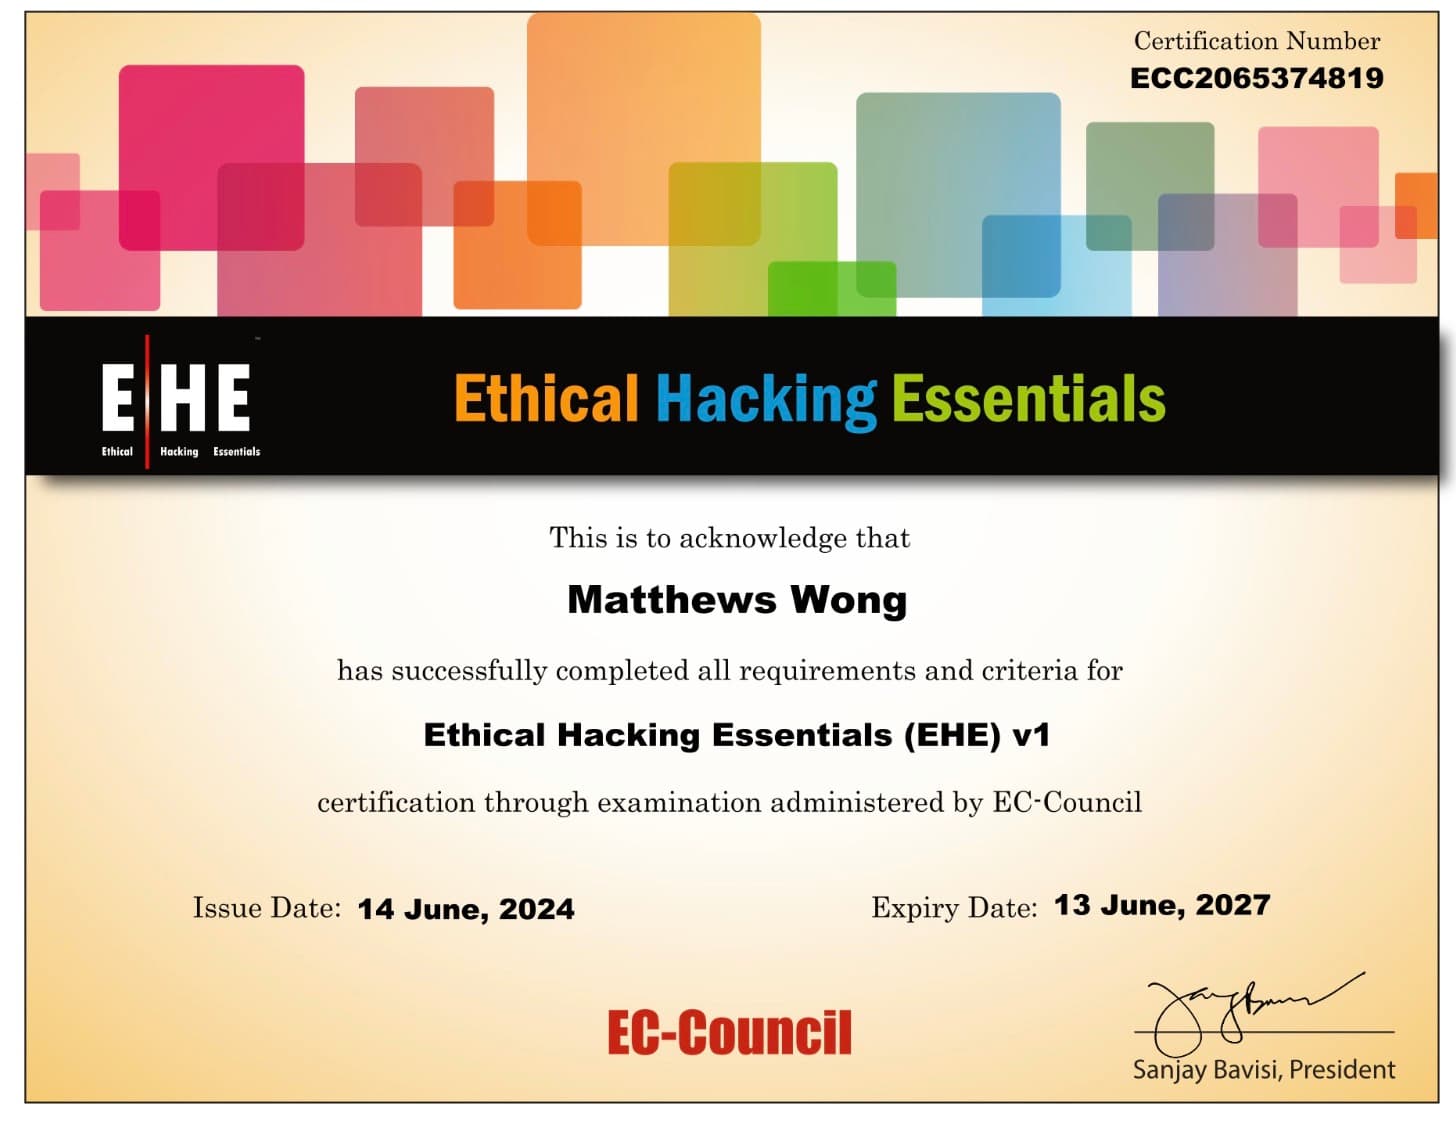
Verified Credential Access
Open the official certificate issued by EC-Council to review credential authenticity and verification details.